 Oct 28, 2026
Replit’s Architecture Behind Secure Agent Work
Empower businesses to do more ambitious work with AI in Replit’s Agent Habitat, backed by the security and governance they need.
 Oct 22, 2026
Security vulnerabilities across the internet: How Replit is protecting your business
The vulnerabilities disclosed this week affect software that much of the internet depends on. They create real risks for businesses and more work for the teams responsible for keeping their applications secure. As AI makes more vulnerabilities easy to find, those teams will face more pressure to respond. At Replit, the security of our customers and the software and businesses they are building is our top priority. We’re handling much of the work for them directly: patching infrastructure, updating language tooling, and blocking exploits. Helping you build software also means helping you keep it secure once it’s running. We manage the environment your apps run in. This means we can apply many of these protections without you having to do anything. If you need to republish an app, we’re notifying you directly.
 Aug 17, 2026
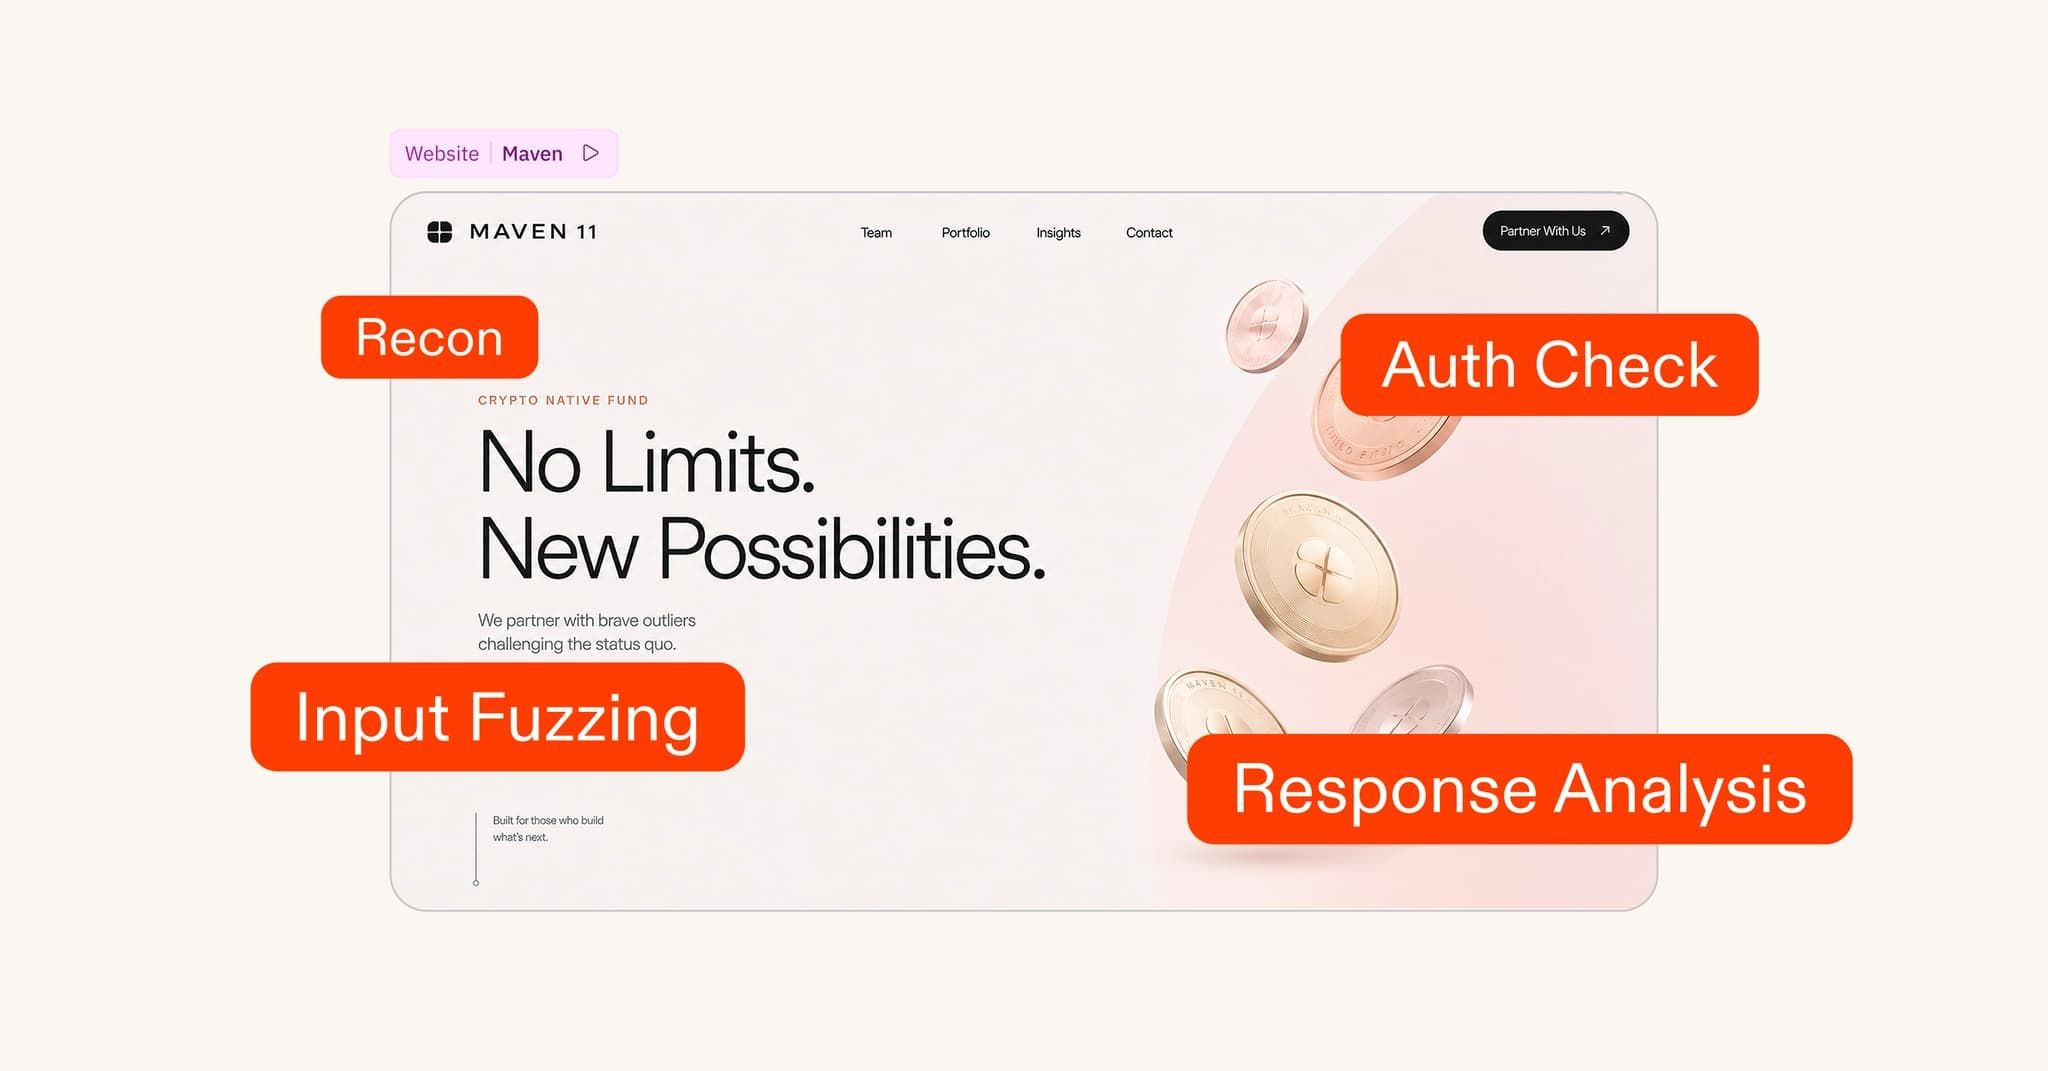
Black-box pen tests on Replit
See how Replit's new black-box pen testing simulates real attacks to find vulnerabilities hidden from code-only scans.
 Aug 16, 2026
Govern Replit at scale
New Enterprise Governance tools for Replit
 Apr 20, 2026
Defense in Depth: How Replit Secures Every Layer of the Vibe Coding Stack
Defense in Depth: How Replit Secures Every Layer of the Vibe Coding Stack Vibe coding is changing how software gets built. But as AI agents write more of our code, the question security teams are asking has shifted from "Can AI build this?" to "Can I trust what AI builds?". At Replit, we believe the answer has to be yes, not through blind faith, but through architecture. Every layer of the Replit infrastructure where customer code runs, from the development sandbox to the production deployment, is designed with defense in depth. The Replit platform itself, our control plane, is also implemented with these principles in mind. No single control is the last line of defense. Every layer assumes the one above it might fail. This post is a detailed walkthrough of how we think about security across the stack, written for the people who need to evaluate it: CISOs, security engineers, and teams considering Replit for production workloads. Zero Trust as a Foundation Replit adheres to Zero Trust Architecture principles across our internal infrastructure. Concretely, that means:
 Dec 4, 2025
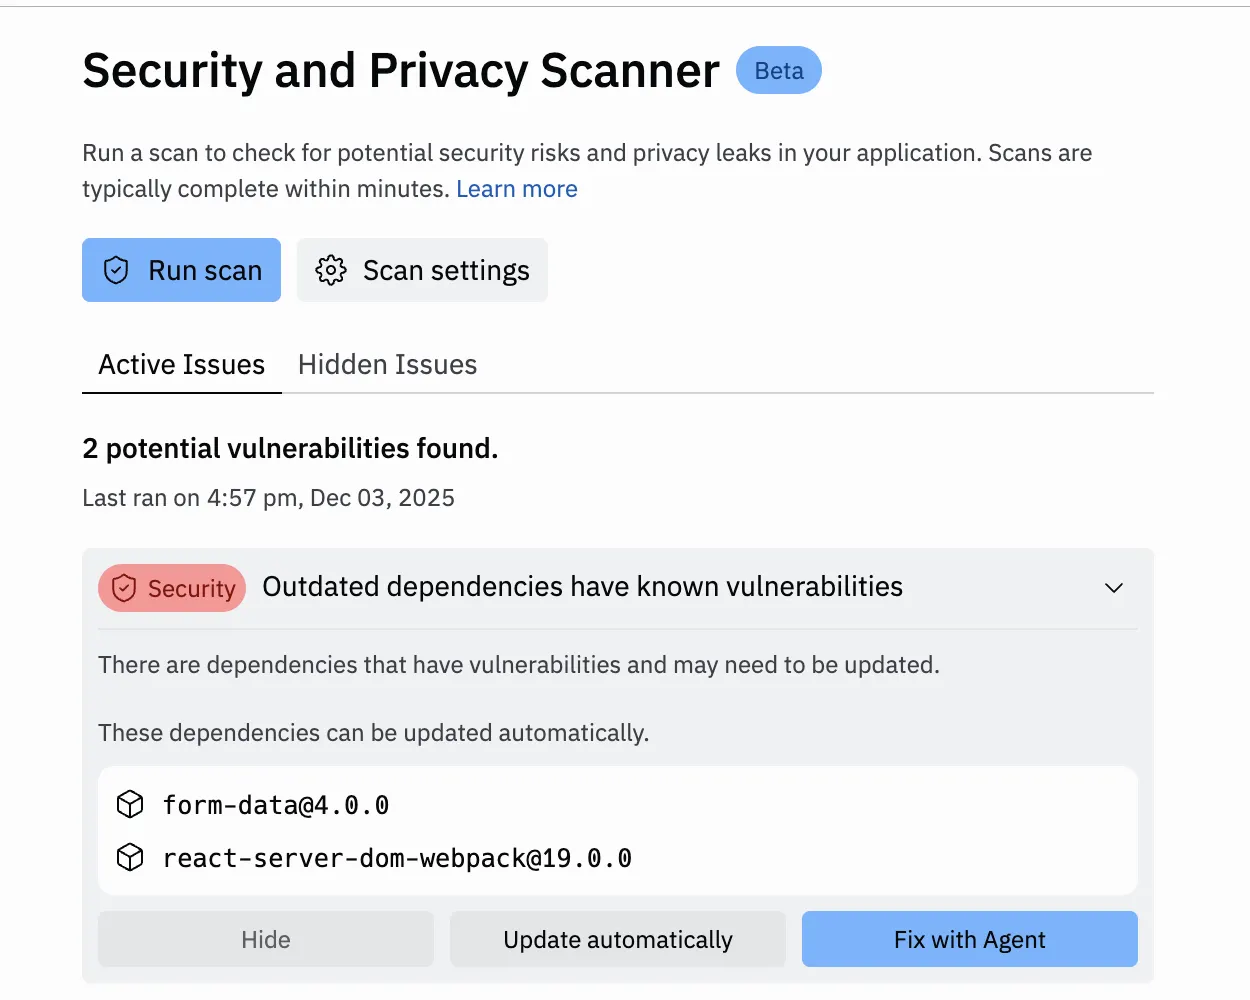
Critical Security Vulnerability in React Server Components
Yesterday, a critical vulnerability in React Server Components was announced that affects both reactjs and Vercel’s NextJs. The vulnerability is present in versions 19.0, 19.1.0, 19.1.1, and 19.2.0 of: react-server-dom-webpack react-server-dom-parcel react-server-dom-turbopack and Next.js with versions ≥14.3.0-canary.77, ≥15 and ≥16.
 Sep 18, 2025
How Replit is Protecting You From the "Shai-Hulud" Worm
Recently, a sophisticated supply chain attack compromised the popular @ctrl/tinycolor NPM package, which receives over 2 million weekly downloads, alongside hundreds of other packages in what has dubbed the "Shai-Hulud" attack. The attack's worm-like behavior and automated credential harvesting capabilities make it an extremely severe JavaScript supply chain attack, and the first worm of its kind affecting npm packages, exposing sensitive developer credentials across the industry. Unlike traditional malware that targets individual systems, this attack specifically compromises JavaScript packages that developers install in the projects. When the package is being installed, it executes the malicious npm postinstall lifecycle script bundle.js . The script scans the developer’s codebase for sensitive credentials like Github tokens and NPM authentication tokens. The token credentials are then used to inject the malware into more packages under the compromised developer’s account. It is creating a rapidly spreading infection across the NPM ecosystem. Since Replit controls the network environment where users’ development environments run, we were able to take immediate action to protect our users. To ensure Replit users don't have their credentials stolen, we blocked the exfiltration endpoint across all development environments. This measure prevents the compromised packages from transmitting harvested credentials to the attacker's webhook endpoint, neutralizing the threat. In addition to this, we've upgraded our Security Scanner to detect malicious code in our users' environments. It now includes a Malicious File Detection feature: it detects known malicious files from attacks, including the the files which indicate compromise from the Shai-Hulud worm.
- Jun 9, 2023
Keeping Your API Keys Safe
Replit gives you the power to both build your own applications and to leverage powerful third party services through their APIs. By integrating third party services into their Repls, Replit users have unlocked a diverse range of capabilities such as speech to text, video livestreaming, embedding data into AI applications, and even tracking Amtrak trains. Integrating a third-party service into your Repl usually involves acquiring an API key or token from the third party that uniquely identifies you and your app. It’s important to keep this API key secret because if it is leaked and used by someone else, they could misuse it while impersonating you. You could find yourself losing your API access, or even incurring unauthorized charges. We saw this need and developed tooling around it for you. Replit makes it easy for you to protect your API keys, by using Secrets. When you add your API key as a Secret, you make sure that it won’t be visible to others who view your Repl’s code, and won’t be included if anyone else forks your Repl. With the recent explosion of interest in AI, there has been a corresponding rise in the theft of OpenAI API keys in particular. Replit is doing its part to make sure that our users don’t become victims of this crime. We have been a partner of OpenAI’s since 2021 and care deeply about AI development and security.